General

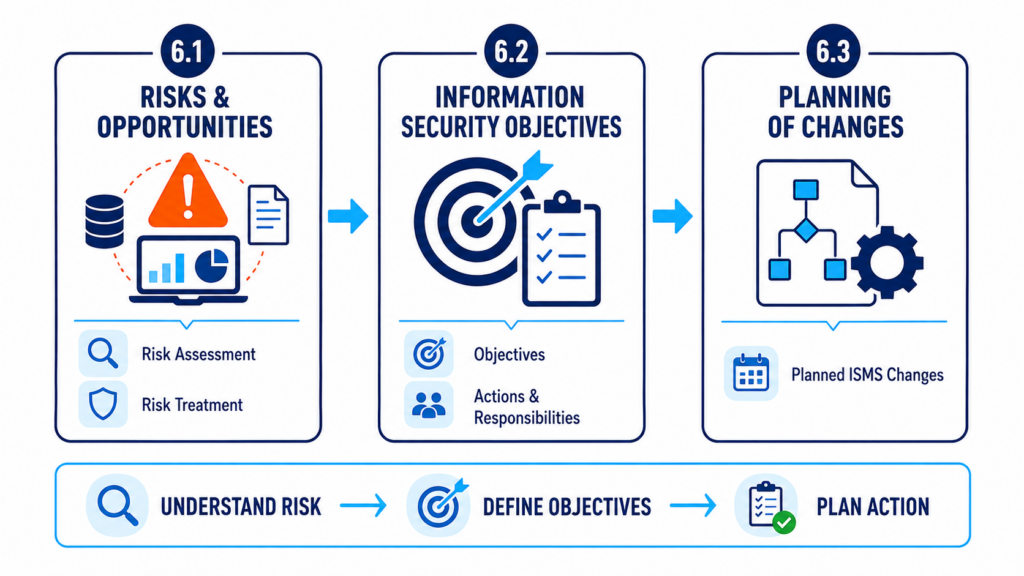
ISO IEC 27001 Clause 6 Planning overview showing risks and opportunities, information security objectives and planning of ISMS changes

ISO/IEC 27001 Clause 6 Explained – Planning for Information Security

ISO/IEC 27001 Clause 6 Explained – Planning for Information Security Effective information security requires more than identifying risks or defining security policies. Organizations also need a structured approach for deciding what needs to be addressed, which objectives should be achieved and how planned changes to the Information Security Management System are implemented. This is the …

ISO/IEC 27001 Clause 6 Explained – Planning for Information Security Read More »
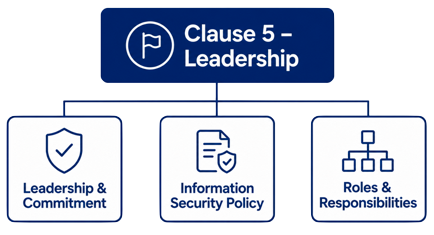
ISO IEC 27001 Clause 5 structure showing leadership and commitment, information security policy, and organizational roles and responsibilities

ISO/IEC 27001 Clause 5 Explained – Leadership

ISO/IEC 27001 Clause 5 Explained – Leadership An effective Information Security Management System cannot be established by the IT department alone. Information security affects business processes, employees, suppliers, customers, technology, strategic decisions, and ultimately the entire organization. For this reason, ISO/IEC 27001 Clause 5 – Leadership places clear responsibilities on top management. Leadership must ensure …

ISO/IEC 27001 Clause 5 Explained – Leadership Read More »

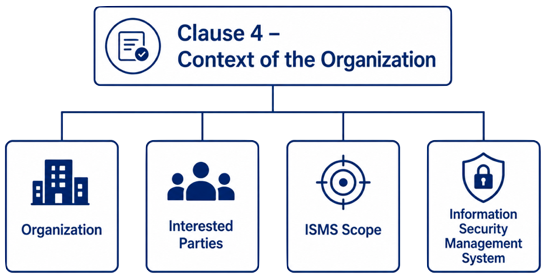
ISO IEC 27001 Clause 4 structure showing organizational context, interested parties, ISMS scope and establishment of the Information Security Management System

ISO/IEC 27001 Clause 4 Explained – Context of the Organization

ISO/IEC 27001 Clause 4 Explained – Context of the Organization Before an organization can effectively manage information security risks, implement security controls, or define information security objectives, it first needs to understand the environment in which it operates. What business activities need protection? Which internal and external factors influence information security? Who are the relevant …

ISO/IEC 27001 Clause 4 Explained – Context of the Organization Read More »

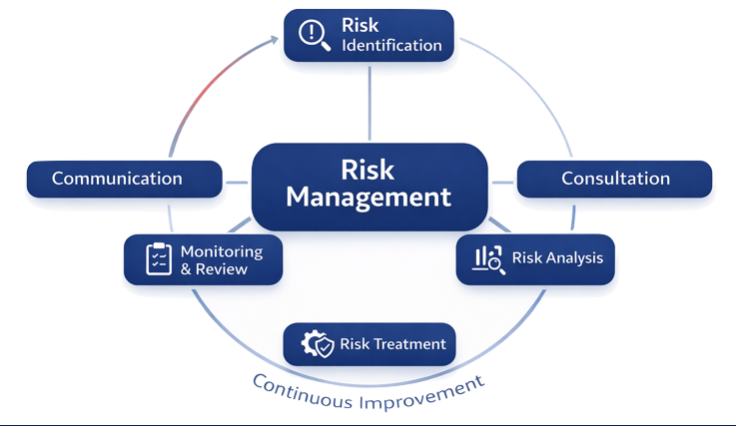
ISO 31000 risk management process including risk identification analysis evaluation treatment and monitoring

ISO 31000 Explained – Risk Management Principles

ISO 31000 Explained – Risk Management Principles Risk is a part of every organization. Whether developing safety-critical systems, managing cybersecurity threats, launching new products, or running daily business operations, organizations constantly face uncertainty. The challenge is not eliminating all risks—this is rarely possible. Instead, successful organizations identify, assess, and manage risks in a structured and …

ISO 31000 Explained – Risk Management Principles Read More »

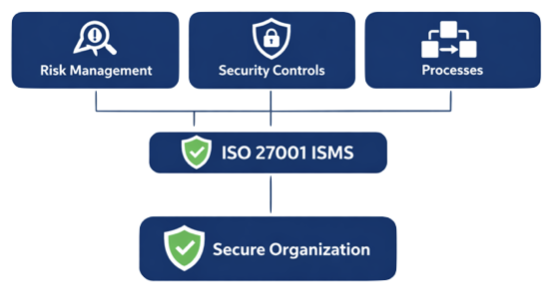
ISO 27001 information security management system with cybersecurity governance and risk management concepts

ISO 27001 Explained – Information Security Management Systems

ISO 27001 Explained – Information Security Management Systems Information has become one of the most valuable assets of modern organizations. Whether it is customer data, intellectual property, financial records, business strategies, or engineering documentation, organizations depend on secure and reliable information to operate effectively. At the same time, cyberattacks, data breaches, insider threats, and regulatory …

ISO 27001 Explained – Information Security Management Systems Read More »

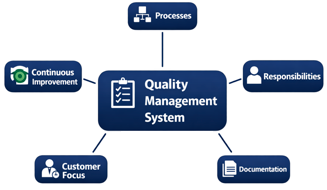
Key elements of ISO 9001 including process management continuous improvement and quality assurance

ISO 9001 Explained – Quality Management Systems

ISO 9001 Explained – Quality Management Systems Quality management plays an essential role in modern organizations. Whether in engineering, manufacturing, software development, healthcare, or services, companies must ensure that their processes consistently deliver reliable results. As organizations grow in complexity, maintaining process consistency, customer satisfaction, and operational efficiency becomes increasingly challenging. This is where ISO …

ISO 9001 Explained – Quality Management Systems Read More »

Shopping Cart
Cookie Consent with Real Cookie Banner